At a leading NBFC, Jimit Shah frames cybersecurity as the discipline that connects systems, vendors, privacy, AI and boardroom judgment to the confidence customers place in a financial institution.
Jimit Shah and the Trust Chain Behind Modern Finance
Nov 21, 2026
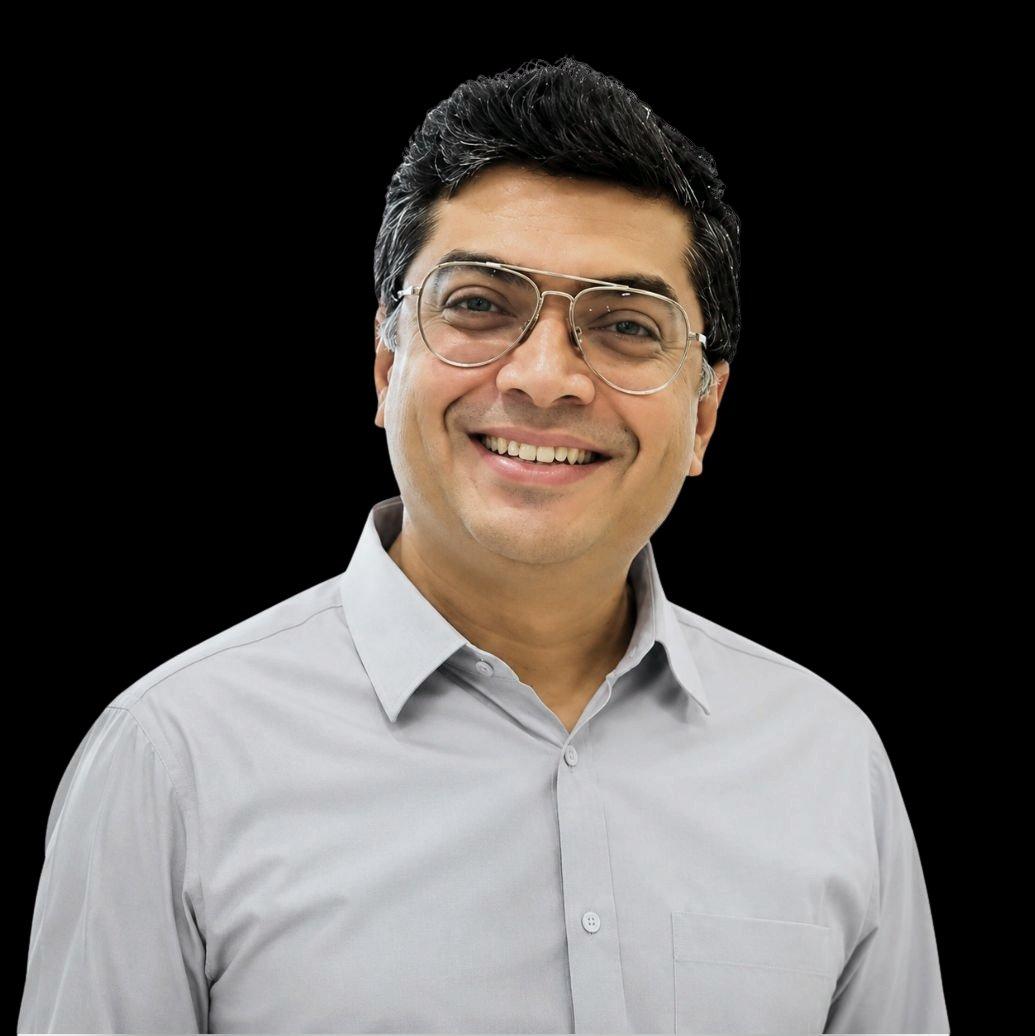
Jimit Shah
Chief Information Security Officer · A leading NBFC
Mumbai, India
A loan processing application rarely looks dramatic from the customer’s side. It is usually seen as a set of income proofs, property papers, bank statements, identity records, credit history and family details moving through a process that is expected to be smooth, predictable and safe. Behind that routine transaction sits a concentrated map of someone’s financial life, along with the expectation that the institution receiving it has the maturity to protect what has been shared.
Financial institutions carry confidence every day, often without the customer seeing how much work is required to preserve it. Access reviews, vendor checks, audit trails, privacy processes, board updates, cyber controls and employee awareness may remain invisible to the borrower, yet the relationship still rests on the belief that each responsibility has been taken seriously.
Ask Jimit Shah what cybersecurity ultimately protects, and he comes back to trust before he comes to tools.
“Cybersecurity helps you in building trust.”
For Jimit, that trust is shaped through decisions that sit quietly behind the customer experience: who can access data, how vendors are reviewed, how incidents are escalated, how boards are informed, how privacy becomes process, and how leaders behave when speed begins pressing against responsibility. His work as Chief Information Security Officer at a leading NBFC sits exactly at that intersection, and his earlier career across data centres, SAP security, audit, governance and financial-services security leadership has given him a rare view of the institutional chain through which risk travels.
What Systems Teach Before Leadership Does
Jimit began his career close to the physical and operational side of technology, where systems are less abstract and more immediate. Data centres, servers, racks, networks and SAP security gave him a ground-level understanding of how things actually run, how dependencies appear, and how small technical gaps can create larger operating consequences. Audit and governance later changed the angle of the work, moving him from keeping systems active to understanding whether the processes around them had enough discipline.
He explains the shift through the three lines of defence in a way that feels practical rather than textbook-heavy. Operations is where the work happens. Governance sits one level above it, making sure management intent reaches day-to-day execution. The review layer comes later, asking whether the discipline written into a process is visible when the work is actually done. His road-signal analogy makes the idea easy to grasp: drivers move traffic, signals and traffic police create order, and the challan becomes the reminder that discipline has consequences.
Those early years gave his leadership a base that is difficult to acquire from dashboards alone. A leader who has spent time with systems knows that risk rarely announces itself neatly. It sits in access rights, delayed patches, weak handovers, unclear ownership, hurried approvals and small gaps that appear manageable until they begin moving across teams and processes.
The CISO role brings those experiences into a larger field of consequence, where a technical weakness can become a business concern, a business concern can become a customer-confidence issue, and a customer-confidence issue can eventually reach the boardroom, the regulator and the institution’s reputation.
“As soon as there is a shift from operations to leadership, your ownership bucket becomes much bigger.”
His idea of an “ownership bucket” captures the shift every technical leader eventually has to make. Earlier in a career, a mistake may belong to a system, a configuration or a process; in leadership, the same mistake begins touching people, customers, regulators and institutional credibility. The work expands from finding the weakness to owning the effect it can create.
Role changes have also shaped the way he learns. He says he enters every new responsibility like a first-year student, a habit with practical value because a new mandate can punish leaders who carry too much certainty from an older role. Technology changes, institutions differ, business pressures shift, and people respond to risk in different ways, so learning again becomes part of staying useful.
The Boardroom Test
Jimit’s first board meeting in 2019 forced a different kind of reckoning. Years of working with firewalls, routing, switching and systems had prepared him to understand risk, yet the room needed something else from him: language that could help directors judge the seriousness of the issue without being pulled into the machinery of it.
“The conversion of technical language into understandable English is a nightmare.”
He remembers the early reactions clearly. Board members wanted him to explain again, simplify and use language they could understand. The first few meetings, by his own description, were difficult enough to become a form of education. Technical mastery had carried him to the room; the room then taught him that mastery has limited value until it can be translated.
For many security leaders, that transition is one of the harder tests of growth. Technical vocabulary can be precise for engineers and opaque for decision-makers, and a board needs enough understanding to ask the right questions, sense the seriousness of the issue and decide whether the institution is responding with adequate depth. The pressure is subtle because over-explaining can lose the room and under-explaining can create false comfort.
Jimit’s boardroom thinking has become more disciplined over time. In BFSI, he says a completely clean cyber dashboard is almost a dream because the environment is always moving: new vulnerabilities appear, business priorities shift, external threats evolve, vendors change, and internal behaviour creates new exposures.
A useful board conversation, in his view, should reach three questions: Are we cyber safe? Are we protecting customer trust? Is there anything concerning that needs to be highlighted?
“Is there anything concerning that you want to highlight?”
Many concerns do not fit neatly inside a dashboard. A CISO, CTO or data privacy officer may sense a risk that has not yet become a headline metric, and good governance gives that concern a route into the room before urgency takes over. The boardroom changed the unit of his work: cybersecurity had to move from technical accuracy into institutional judgment.
The Trust Chain Inside a Boundaryless Enterprise
A digital financial institution depends on a long chain of trust. The customer sees a loan application, a document upload, a service request or a payment; behind that visible interaction sit systems, access rights, process owners, vendors, auditors, regulators, privacy obligations and leadership choices.
Jimit’s thinking moves along that chain. Security may begin with technology, but it gains meaning when it protects the confidence behind a customer relationship. A customer may never know which systems touch the application, which partner supports the workflow or which internal approval allowed access. The expectation remains clear: the institution should know, control and account for that movement.
Leadership behaviour decides how seriously those layers are treated. Jimit believes teams absorb the standards they see at the top.
“Whatever style the leader adopts, usually his or her team will also follow the same approach.”
Security becomes difficult when it touches speed, cost or a commercial timeline. A project team may want to launch quickly, a business leader may see security review as friction, and a vendor may push for faster approval. Jimit’s instinct is to bring people along, especially those who have not yet understood why security matters to the business.
The challenge has become sharper as enterprises have become more boundaryless. Jimit describes the present operating environment as one where institutions want systems to “go live as of yesterday,” and that urgency often depends on partnerships, vendor networks and external technology ecosystems. Post-Covid digitisation added another layer to that challenge: shadow IT was already difficult for security teams; shadow AI has made the perimeter even less visible. The question for a CISO is now about how far the institution’s standards can travel across partners, tools and behaviours that sit beyond the traditional legal perimeter.
The Risk After the Risk Looks Closed
Large institutions can begin to feel safe when the visible marker has been completed. A requirement may be closed, a dashboard may look acceptable, a vendor relationship may appear complete, or an AI-generated answer may sound convincing. The surface can settle before the risk has actually left the system.
Compliance is the most familiar example. Jimit respects its role because regulatory pressure creates urgency: teams move faster, budgets get discussed, evidence gets created and priorities become clearer when there is a formal requirement, a deadline, a review or a consequence.
“It may be effective for compliance, but it may not be effective in design.”
A closed requirement can make an organization feel safer than it actually is. Jimit’s concern is the space between what has been evidenced and what has been strengthened, because after a review is completed, the more important question is whether the process is now better, whether ownership is clearer, and whether the same weakness can still return through another part of the system.
Vendor exit carries the same discipline. Businesses often put more energy into onboarding because it helps work begin, while exit receives less attention because the relationship appears finished, even though access, data, knowledge, process habits and dependency can remain active long after the contract is closed.
“People tend to ignore the exit because they feel that once we have exited, we are done and dusted.”
During the conversation, Jimit begins to reach for a specific example and then stops himself because the session is recorded. The pause is revealing in a profession where the most useful examples are often the ones that cannot be spoken casually. He then turns to a public illustration around sensitive material disposal, using it to show how easily an organization can assume completion once a formal process appears to have ended.
Vendor selection, in his view, resembles entering a long-term relationship because a vendor is rarely a detached service provider in a digital enterprise. It often becomes part of how the institution serves customers, manages data and sustains operations. Weak alignment at the beginning can create difficulty later, and weak exit discipline can allow risk to remain active after the business has mentally moved on.
“You can outsource a service, but you can never outsource accountability.”
That principle becomes especially important in a boundaryless enterprise. A partner may run the process, host the system, manage a workflow or support an application, but the customer’s trust still sits with the institution. The risk cannot be transferred simply because the work has moved outside the organization’s walls.
AI introduces a newer version of the same pressure. An answer can arrive quickly and sound complete, yet the institution still has to ask where the output came from, which data shaped it, what assumption it carried and who remains accountable if the decision goes wrong. The technology may make completion feel faster; the responsibility remains with the organization that chooses to use it.
Privacy, AI and the Human Duty to Think
Privacy has moved from policy language into execution reality. DPDPA has made the issue sharper for Indian institutions because privacy has to move out of documents, intent statements and legal discussions, and into processes, systems, people and budgets.
Jimit sees many failures beginning in the way intent travels. Leadership may begin with the right objective, yet the meaning can weaken across layers: teams may receive partial instructions, budget may not follow ambition, ownership may remain unclear, and technology may be funded while process and people remain underprepared.
He uses a simple analogy. A person may intend to draw an elephant, describe it incompletely, and receive something entirely different. The intention may be correct; the transfer of meaning fails. Privacy implementation can suffer in the same way because a strong statement at the top does not guarantee protection at the operating level.
In a lending context, the stakes are deeply personal. Customer data can include income, identity, family records, banking behaviour, property information and credit history. Protecting such data requires governance that can withstand real business movement.
Jimit sees AI as a present leadership risk because it has already moved from technology discussion into boardroom and business reality. He admits that in 2023 he saw elements of AI as a bubble, then watched the conversation change rapidly through 2024 and 2025, and by 2026 he sees it becoming part of actual business decisions. His larger worry now is dependency: inside an organization, AI becomes dangerous when professionals consume output without questioning the reasoning behind it.
“The biggest risk I foresee because of AI is that AI is making today’s newer generation mindless.”
AI can support research, speed up processes, improve productivity and create new possibilities. The risk appears when the output becomes a substitute for inquiry. A professional who accepts an answer without asking why weakens the very muscle organizations need in uncertain situations.
“If AI makes a failure, it is the failure of the organization.”
AI changes responsibility because machine output can create a false sense of completion. Leaders have to define the purpose clearly before development begins. Jimit warns against moving goalposts during AI projects because shifting the purpose midway forces teams into shortcuts and allows security gaps to enter the system. His design-thinking view is practical: spend serious energy upfront defining the problem, build with discipline, test heavily, and keep human review close to the decision.
What Digital Leaders Can Learn From Jimit Shah’s Operating Lens
Technical depth has to grow into institutional understanding. A leader has to know the system closely enough to see how one weakness can move into customer trust, business continuity and reputation.
Responsibility expands faster than authority. As the role becomes larger, even a small failure has to be read through its effect on people, process and institutional confidence.
Boards need risk in a language they can use. Cybersecurity loses force when it remains trapped in vocabulary that decision-makers cannot translate into action.
A clean dashboard should invite sharper questions. Governance works best when leaders create space for concerns that have not yet become visible metrics.
Compliance should leave the system stronger than it found it. Evidence has value when it points to better design, clearer ownership and stronger behaviour.
Vendor exit deserves the same seriousness as vendor selection. Onboarding begins the dependency; exit decides what remains behind.
Privacy depends on the quality of execution. A policy promise has to survive communication, funding, process design and day-to-day ownership.
AI should strengthen human judgment. A faster answer becomes risky when the organization no longer knows how to question it.
Professional growth begins with why. Skill becomes leadership when people understand the reason behind the work they perform.
Ethics has to survive power. Titles may change the size of the decision, but they should not change the person’s moral standard.
Capability, Ethics and the Loan Processing Application
Jimit’s view on professional growth is rooted in depth. Credentials can help, although the real formation happens closer to the work: in long hours with systems, in conversations with seniors, in mistakes that teach judgment, and in the willingness to ask why until the process begins to make sense.
He worries about professionals who know what they are doing and cannot explain why they are doing it.
“As soon as you start questioning everything with why, you grow in your learning.”
His mathematical example is simple. Two plus two is four. Two multiplied by two is also four. Reaching the right result is useful; understanding the route to that result is what turns work into judgment.
Mid-career professionals face their own pressure because they sit between execution teams and senior leaders, carrying questions upward and decisions downward. Jimit values the 5W1H habit because it helps them slow the moment down, understand what is being asked, and avoid moving half-understood issues into the next layer of the organization. He also cautions against rushing leadership, especially when people want to “hop, skip and jump” into senior roles without burning their hands deeply enough in the work.
His deepest leadership lesson is ethical.
“Whatever position you are in, your ethics, morals and honesty should remain the same.”
Power can change behaviour. Titles can change how people see themselves. Authority can make shortcuts look easier. Jimit’s standard is direct: the chair may change, but the person’s ethics should not.
At a leading NBFC, that belief meets a very practical form of responsibility. A loan processing application contains far more than documents. It carries identity, income, family context, property information, credit behaviour and the confidence of a customer who may never know how many systems, people and partners touch that data.
The institution has to deserve that confidence before anything goes wrong. Cybersecurity, in Jimit Shah’s telling, helps keep attention on the places where trust can weaken quietly. A leftover access right, a poorly closed vendor relationship or an AI answer accepted too quickly can each become the kind of invisible weakness that customers only notice when confidence has already been damaged.
His mandate as CISO sits inside that trust chain. The work is to keep institutional ambition answerable to responsibility, especially when speed, partnership or new technology makes progress feel easier than caution. The CISO’s office becomes one of the places where an institution asks a harder question of itself: whether the system is strong enough for the confidence customers place in it every day.
The loan processing application, then, becomes more than an opening image. It is the test of the institution’s character, because every invisible handoff behind it asks whether the organization is disciplined enough, thoughtful enough and honest enough to deserve the trust already placed in it.